PulseAugur
实时 15:39:36
English(EN) Semantic Layer vs MCP: Why Direct ERP Write Access Is an Enterprise Security Risk

企业AI安全:MCP写入权限风险被忽视

通过模型上下文协议(MCP)将大型语言模型(LLMs)直接连接到企业系统存在重大的安全风险,特别是当恶意提示可能触发意外写入操作时。虽然语义层提供了安全的只读接口,但MCP允许写入权限,从而创建了一个可能导致数据篡改或系统中断的攻击面。为减轻这些风险,任何MCP写入路径都必须有一个三层治理控制系统,包括提示验证、MCP服务器上的严格模式执行以及关键数据操作的强制性人工审批环节。 AI

影响 强调了将LLMs连接到企业写入操作中的关键安全漏洞,为安全的AI集成提供了必要的强大治理层。

排序理由 文章讨论了一个特定的协议(MCP)及其与LLMs和企业系统结合使用时的安全影响,这属于AI工具和基础设施安全范畴。

在 dev.to — MCP tag 阅读 →

AI 生成摘要 · Google Gemini · 来自 1 个来源。 我们如何撰写摘要 →
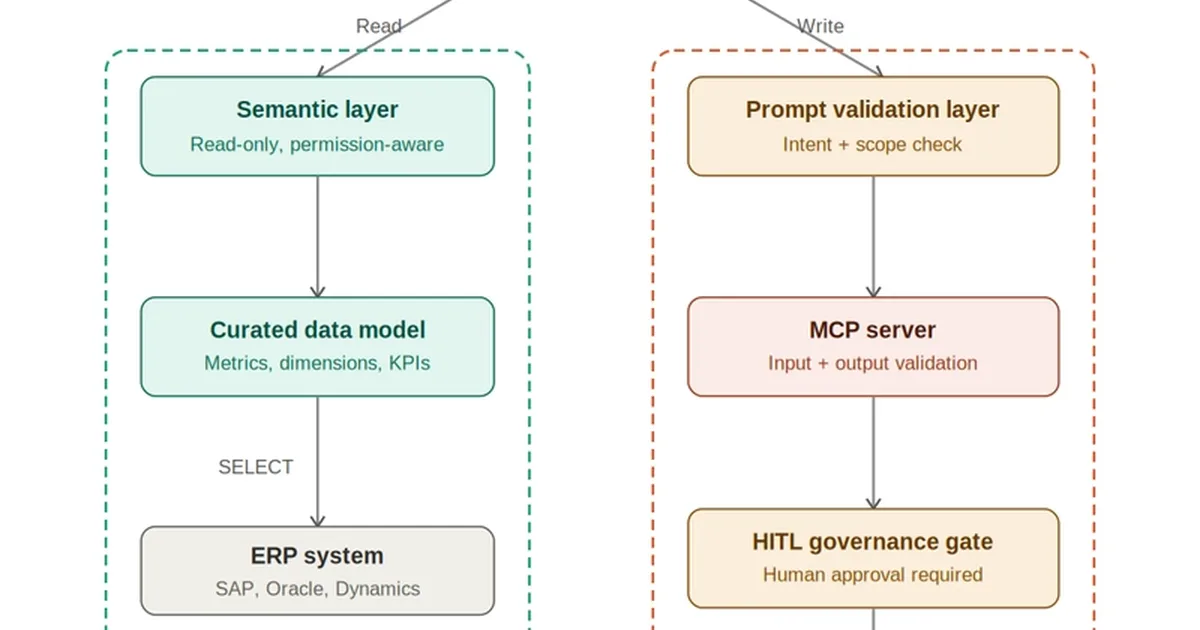
企业AI安全:MCP写入权限风险被忽视

本文如何被排名

Signal score
0 / 100
Composite score across the factors below. Higher = stronger signal that this story matters right now.
Newsworthiness bucket
Tool
文章讨论了一个特定的协议(MCP)及其与LLMs和企业系统结合使用时的安全影响,这属于AI工具和基础设施安全范畴。
Source corroboration
Single-source cluster
Only one publisher covered this so far. Single-source stories can still rank when the publisher is high-authority, but they lack cross-source corroboration.
Topics
safety, product, infra
Editorial topic classification. Feeds into how the story surfaces on /topic/<slug> hub pages and into the per-entity coverage mix.
AI-industry relevance
High
Clearly on-topic for AI-industry coverage.
Story freshness
91 days old
Aged out of breaking-news scoring windows; ranking reflects the durable signal from the full source set.

完整方法见我们的编辑标准

报道来源 [1]

  1. dev.to — MCP tag TIER_1 English(EN) · dnyandeo bharambe ·

    Semantic Layer 与 MCP:为什么直接 ERP 写入权限是企业安全风险

    <p>⚠️ <strong>Failure Mode:</strong> Most architects celebrating MCP's ability to connect LLMs directly to enterprise systems are skipping a critical question: what happens when the prompt is malicious? One crafted instruction can execute a real write operation against your ERP w…