PulseAugur
中
实时 09:13:47
English(EN) VMware vCenter CVE-2026-123890 (CVSS 9.8, unauthenticated auth bypass in the Directory Service) was exploited as a zero-day since early September by China-nexus

VMware vCenter 零日漏洞被中国相关组织利用;补丁已发布

一个关键的 VMware vCenter 漏洞 CVE-2026-123890,CVSS 评分为 9.8,被一个名为 Armory Castle 的中国相关组织作为零日漏洞利用。该目录服务中的未经身份验证的授权绕过漏洞自九月初以来一直被积极利用。Broadcom 于 11 月 19 日发布了该漏洞的补丁,敦促用户更新其 vCenter 实例并保护 SSO 管理员帐户。 AI

排序理由 该项目讨论了一个特定的软件漏洞及其利用,以及补丁发布,属于“工具”类别,因为它与软件安全和维护有关。

在 Mastodon — mastodon.social 阅读 →

AI 生成摘要 · Google Gemini · 来自 1 个来源。 我们如何撰写摘要 →
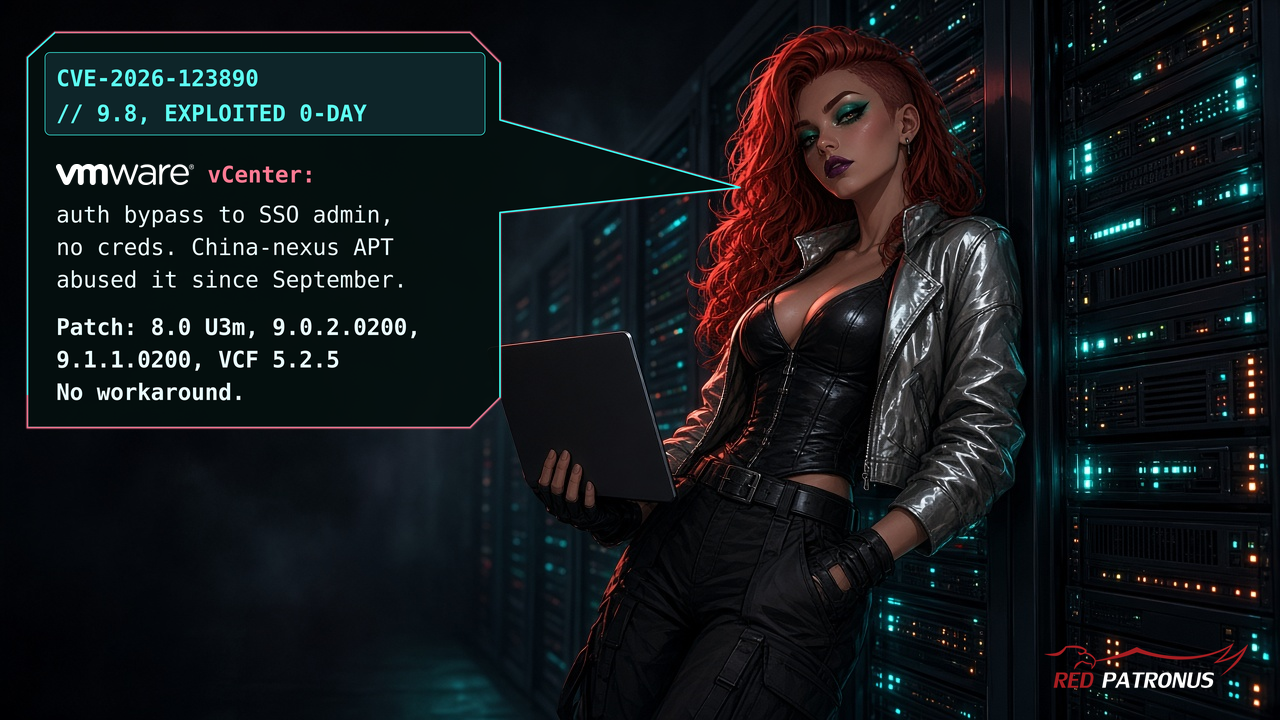
VMware vCenter 零日漏洞被中国相关组织利用;补丁已发布

本文如何被排名

Signal score
2 / 100
Composite score across the factors below. Higher = stronger signal that this story matters right now.
Newsworthiness bucket
Tool
该项目讨论了一个特定的软件漏洞及其利用,以及补丁发布,属于“工具”类别,因为它与软件安全和维护有关。
Source corroboration
Single-source cluster
Only one publisher covered this so far. Single-source stories can still rank when the publisher is high-authority, but they lack cross-source corroboration.
Topics
product, other
Editorial topic classification. Feeds into how the story surfaces on /topic/<slug> hub pages and into the per-entity coverage mix.
AI-industry relevance
Low
Off-topic or adjacent — cluster remains reachable but doesn't surface in AI-industry rankings.
Story freshness
Breaking (< 6h)
Fresh story with cross-source coverage still developing. Ranking may shift as more sources report.

完整方法见我们的编辑标准。

报道来源 [1]

  1. Mastodon — mastodon.social TIER_1 English(EN) · burso ·

    VMware vCenter CVE-2026-123890(CVSS 9.8,目录服务中未经身份验证的身份绕过)自九月初以来被中国相关方作为零日漏洞利用

    VMware vCenter CVE-2026-123890 (CVSS 9.8, unauthenticated auth bypass in the Directory Service) was exploited as a zero-day since early September by China-nexus Armory Castle, per Google/Mandiant. Broadcom shipped fixes in VMSA-2026-0009 on Nov 19. Patch: vCenter 8.0 U3m, 9.0.2.0…