PulseAugur
中
实时 08:24:28

LiteLLM vulnerability CVE-2026-40217 added to CISA KEV list

A critical vulnerability, CVE-2026-40217, affecting LiteLLM has been added to the CISA Known Exploited Vulnerabilities (KEV) catalog. This vulnerability, which has been exploited in the wild, allows for code execution within the proxy process due to a sandbox escape in the custom-code guardrail test endpoint. Users are advised to upgrade to version 1.83.10-stable or later, or to block POST /guardrails/test_custom_code requests at their gateway if an immediate upgrade is not possible. AI

影响 This critical vulnerability in LiteLLM, a tool for simplifying LLM API calls, could impact the security of AI applications relying on it.

排序理由 Security advisory for a specific software tool.

在 Mastodon — mastodon.social 阅读 →

AI 生成摘要 · Google Gemini · 来自 1 个来源。 我们如何撰写摘要 →
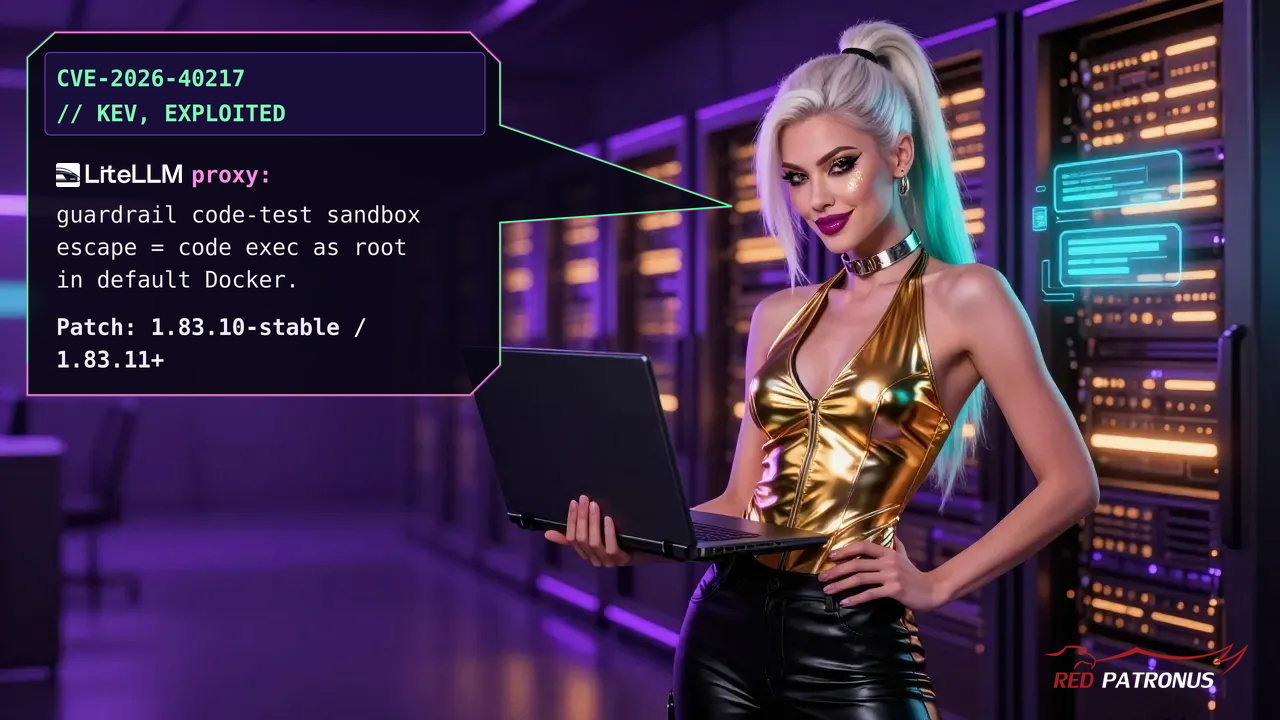
LiteLLM vulnerability CVE-2026-40217 added to CISA KEV list

本文如何被排名

Signal score
14 / 100
Composite score across the factors below. Higher = stronger signal that this story matters right now.
Newsworthiness bucket
Tool
Security advisory for a specific software tool.
Source corroboration
Single-source cluster
Only one publisher covered this so far. Single-source stories can still rank when the publisher is high-authority, but they lack cross-source corroboration.
Topics
product, safety
Editorial topic classification. Feeds into how the story surfaces on /topic/<slug> hub pages and into the per-entity coverage mix.
AI-industry relevance
High
Clearly on-topic for AI-industry coverage.
Story freshness
Breaking (< 6h)
Fresh story with cross-source coverage still developing. Ranking may shift as more sources report.

完整方法见我们的编辑标准。

报道来源 [1]

  1. Mastodon — mastodon.social TIER_1 English(EN) · burso ·

    LiteLLM CVE-2026-40217 昨日(11月18日)被列入CISA KEV:野外利用。自定义代码护栏测试端点中的沙盒逃逸可导致代码执行

    LiteLLM CVE-2026-40217 landed on CISA KEV yesterday (Nov 18): exploited in the wild. A sandbox escape in the custom-code guardrail test endpoint gives code execution in the proxy process, which runs as root in the default Docker image. It needs a proxy-admin credential, so rotate…