PulseAugur
中
实时 19:49:03
English(EN) I pinned each issuer's public key. Then the IdP rotated it.

身份验证系统必须动态获取密钥,而不是固定静态密钥

作者讨论了验证数字身份令牌时遇到的挑战,特别是当身份提供商 (IdP) 的签名密钥被轮换时。最初,作者手动固定了静态公钥,但当 Okta、Keycloak 和 Auth0 等 IdP 更新其密钥时,这种方法失败了。标准的 OpenID Connect (OIDC) 协议通过允许验证者从发行者发布的 JWKS(JSON Web 密钥集)端点动态获取密钥来提供解决方案。这种方法不是固定静态密钥,而是固定受信任的发行者,并在需要时获取他们当前的密钥,并带有缓存机制以避免过多的网络请求。 AI

影响 关于身份验证和密钥管理的这一技术讨论与构建安全、去中心化或联合系统的开发人员相关。

排序理由 文章讨论了与数字身份验证协议和实践相关的技术挑战和解决方案,而不是新的发布或重大的行业事件。

在 dev.to — MCP tag 阅读 →

AI 生成摘要 · Google Gemini · 来自 1 个来源。 我们如何撰写摘要 →
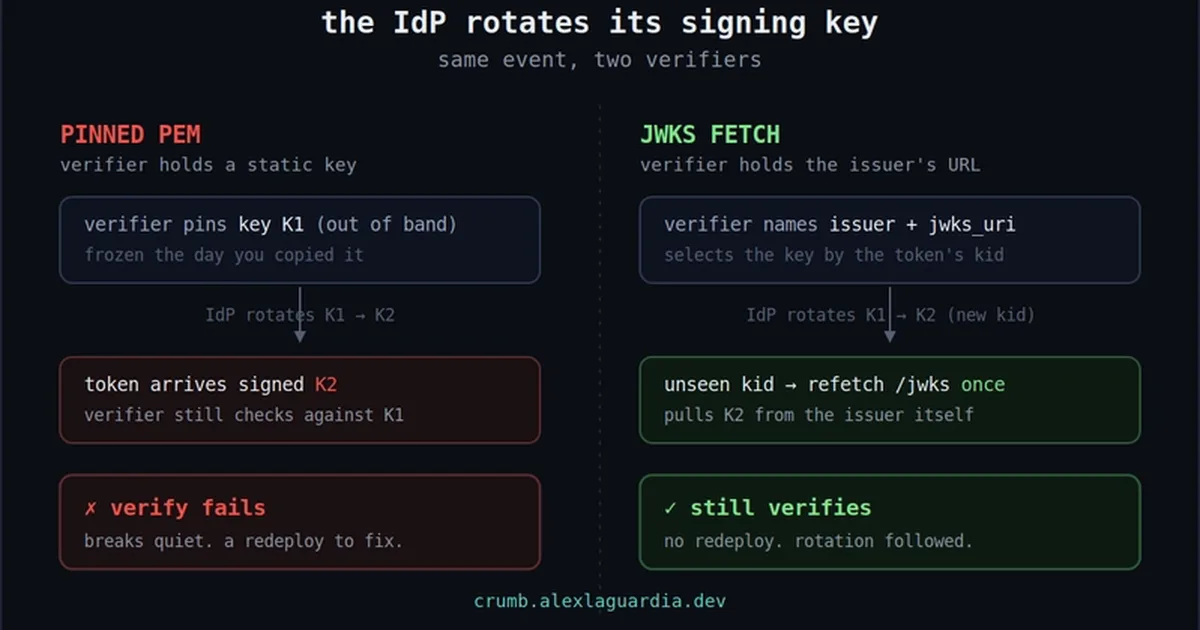
身份验证系统必须动态获取密钥,而不是固定静态密钥

本文如何被排名

Signal score
0 / 100
Composite score across the factors below. Higher = stronger signal that this story matters right now.
Newsworthiness bucket
Commentary
文章讨论了与数字身份验证协议和实践相关的技术挑战和解决方案,而不是新的发布或重大的行业事件。
Source corroboration
Single-source cluster
Only one publisher covered this so far. Single-source stories can still rank when the publisher is high-authority, but they lack cross-source corroboration.
Topics
infra, product
Editorial topic classification. Feeds into how the story surfaces on /topic/<slug> hub pages and into the per-entity coverage mix.
AI-industry relevance
Standard
On-topic for AI-industry coverage; kept in the public index.
Story freshness
96 days old
Aged out of breaking-news scoring windows; ranking reflects the durable signal from the full source set.

完整方法见我们的编辑标准。

报道来源 [1]

  1. dev.to — MCP tag TIER_1 English(EN) · Alex LaGuardia ·

    我固定了每个发行者的公钥。然后 IdP 轮换了它。

    <p>Last time I wrote about keeping the human provable when an agent's delegation chain crosses from one company's identity provider into another's. The verifier walks the chain backward and checks each segment against the key of the issuer that signed it. I ended that post with a…