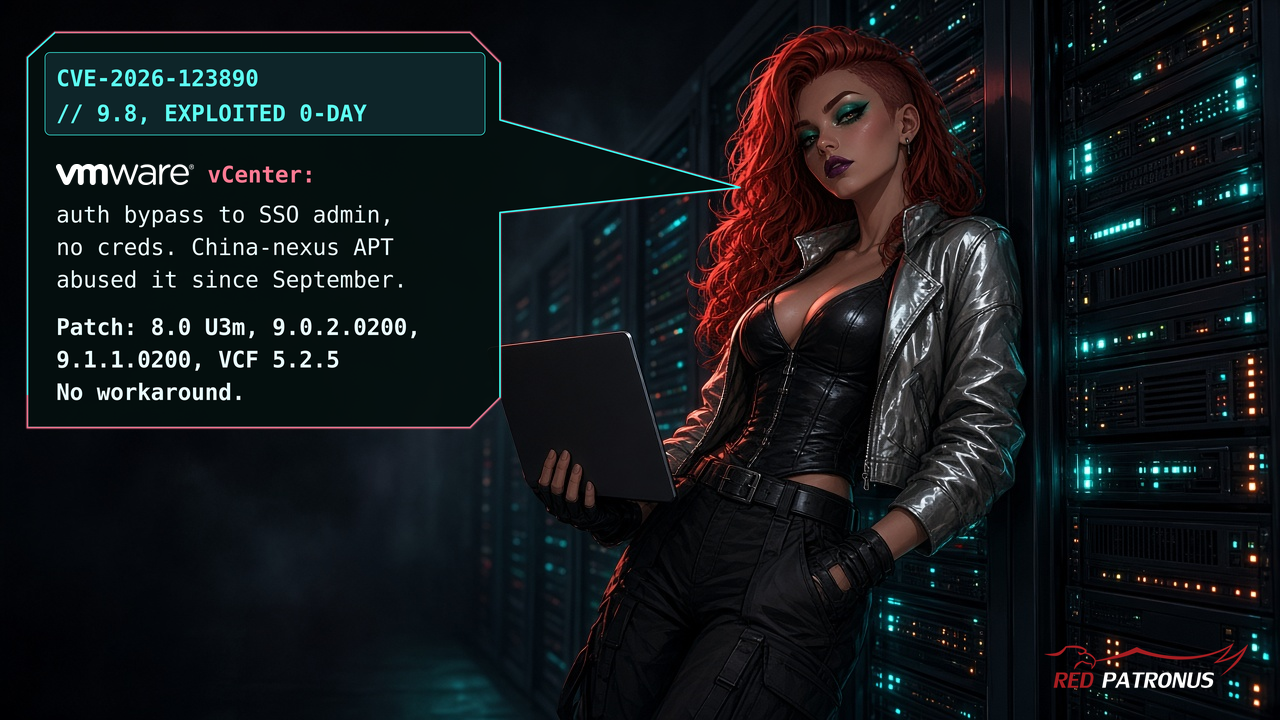
A critical VMware vCenter vulnerability, CVE-2026-123890, with a CVSS score of 9.8, was exploited as a zero-day by a China-nexus group known as Armory Castle. This unauthenticated authorization bypass in the Directory Service was actively exploited since early September. Broadcom released patches for this vulnerability on November 19th, urging users to update their vCenter instances and secure SSO admin accounts. AI
RANK_REASON The item discusses a specific software vulnerability and its exploitation, along with a patch release, which falls under the 'tool' category as it relates to software security and maintenance.
Read on Mastodon — mastodon.social →
AI-generated summary · Google Gemini · from 1 sources. How we write summaries →