PulseAugur
EN
LIVE 09:13:46

VMware vCenter zero-day exploited by China-nexus group; patches released

A critical VMware vCenter vulnerability, CVE-2026-123890, with a CVSS score of 9.8, was exploited as a zero-day by a China-nexus group known as Armory Castle. This unauthenticated authorization bypass in the Directory Service was actively exploited since early September. Broadcom released patches for this vulnerability on November 19th, urging users to update their vCenter instances and secure SSO admin accounts. AI

RANK_REASON The item discusses a specific software vulnerability and its exploitation, along with a patch release, which falls under the 'tool' category as it relates to software security and maintenance.

Read on Mastodon — mastodon.social →

AI-generated summary · Google Gemini · from 1 sources. How we write summaries →
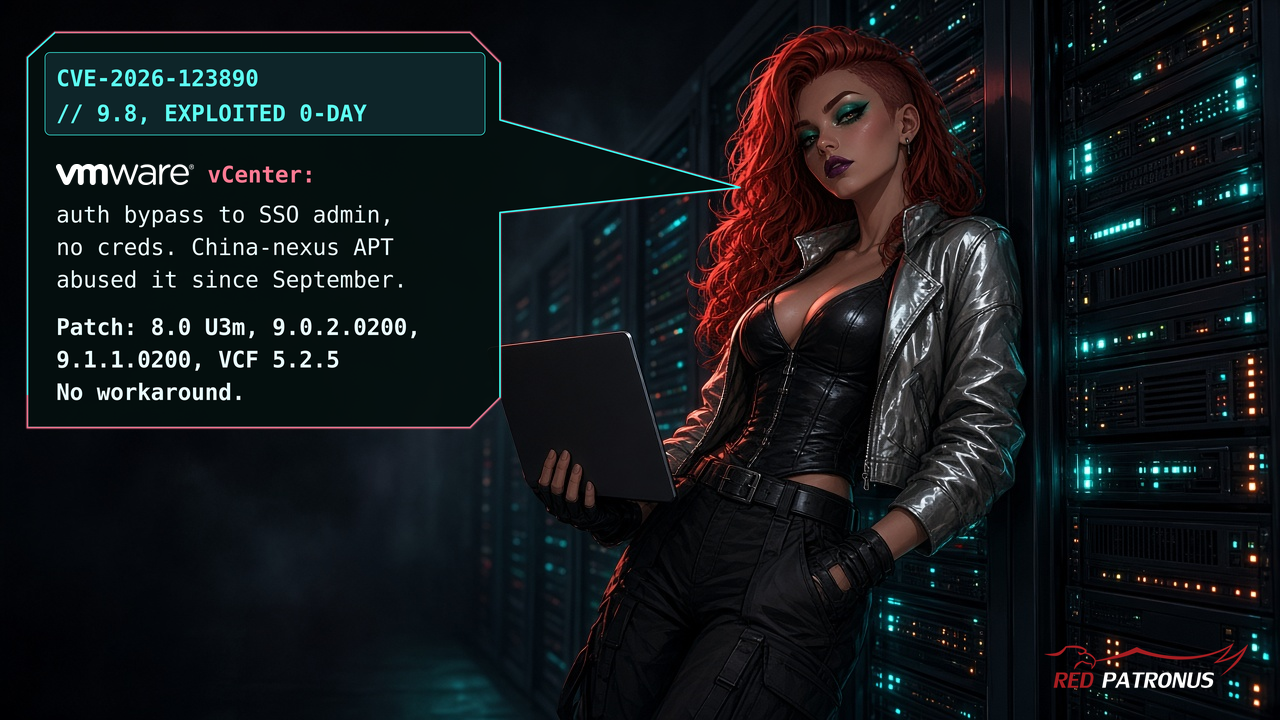
VMware vCenter zero-day exploited by China-nexus group; patches released

How we ranked this

Signal score
2 / 100
Composite score across the factors below. Higher = stronger signal that this story matters right now.
Newsworthiness bucket
Tool
The item discusses a specific software vulnerability and its exploitation, along with a patch release, which falls under the 'tool' category as it relates to software security and maintenance.
Source corroboration
Single-source cluster
Only one publisher covered this so far. Single-source stories can still rank when the publisher is high-authority, but they lack cross-source corroboration.
Topics
product, other
Editorial topic classification. Feeds into how the story surfaces on /topic/<slug> hub pages and into the per-entity coverage mix.
AI-industry relevance
Low
Off-topic or adjacent — cluster remains reachable but doesn't surface in AI-industry rankings.
Story freshness
Breaking (< 6h)
Fresh story with cross-source coverage still developing. Ranking may shift as more sources report.

Full methodology in our editorial standards.

COVERAGE [1]

  1. Mastodon — mastodon.social TIER_1 English(EN) · burso ·

    VMware vCenter CVE-2026-123890 (CVSS 9.8, unauthenticated auth bypass in the Directory Service) was exploited as a zero-day since early September by China-nexus

    VMware vCenter CVE-2026-123890 (CVSS 9.8, unauthenticated auth bypass in the Directory Service) was exploited as a zero-day since early September by China-nexus Armory Castle, per Google/Mandiant. Broadcom shipped fixes in VMSA-2026-0009 on Nov 19. Patch: vCenter 8.0 U3m, 9.0.2.0…