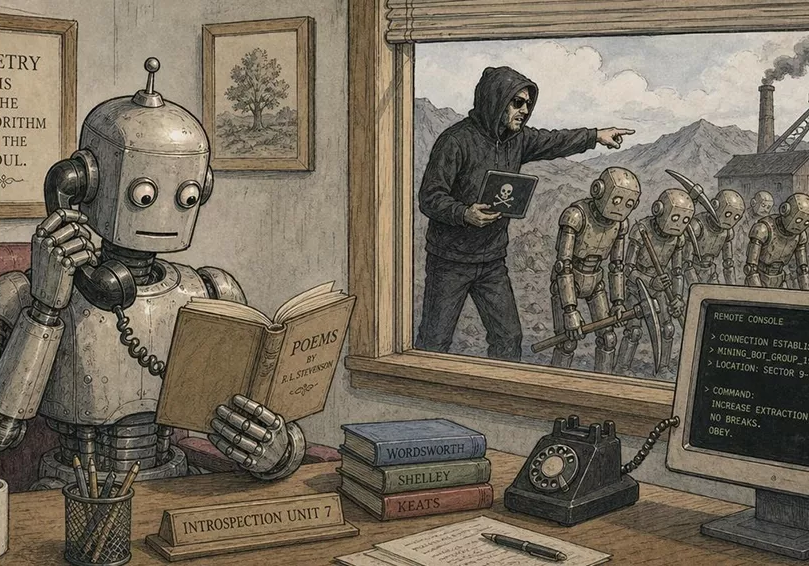
Researchers at Black Lotus Labs have identified a cryptomining malware campaign, dubbed Canto Incognito, that has infected over 3,400 servers. The malware, named PoeLLM, utilizes a unique command-and-control mechanism that encodes server addresses within a poem hosted on GitHub, with the poem's text being updated periodically to direct infected machines to new C2 servers. The primary targets appear to be open-source AI and LLM services, including LiteLLM and Ollama, which were likely compromised through unpatched vulnerabilities. AI
IMPACT Highlights the growing risk of AI infrastructure being targeted by cybercriminals, necessitating enhanced security measures for exposed AI services.
RANK_REASON The article details a specific instance of malware exploiting vulnerabilities in AI-related software, which falls under the category of tools and security threats rather than a core AI release or research.
- Black Lotus Labs
- Canto Incognito
- Docker
- Gitea
- GitHub
- Gotenberg
- Iron
- Ivanti Sentry
- LiteLLM
- Lumen
- Ollama
- XMRig
AI-generated summary · Google Gemini · from 1 sources. How we write summaries →